SensorFu Beacon: HTTP Escape Test
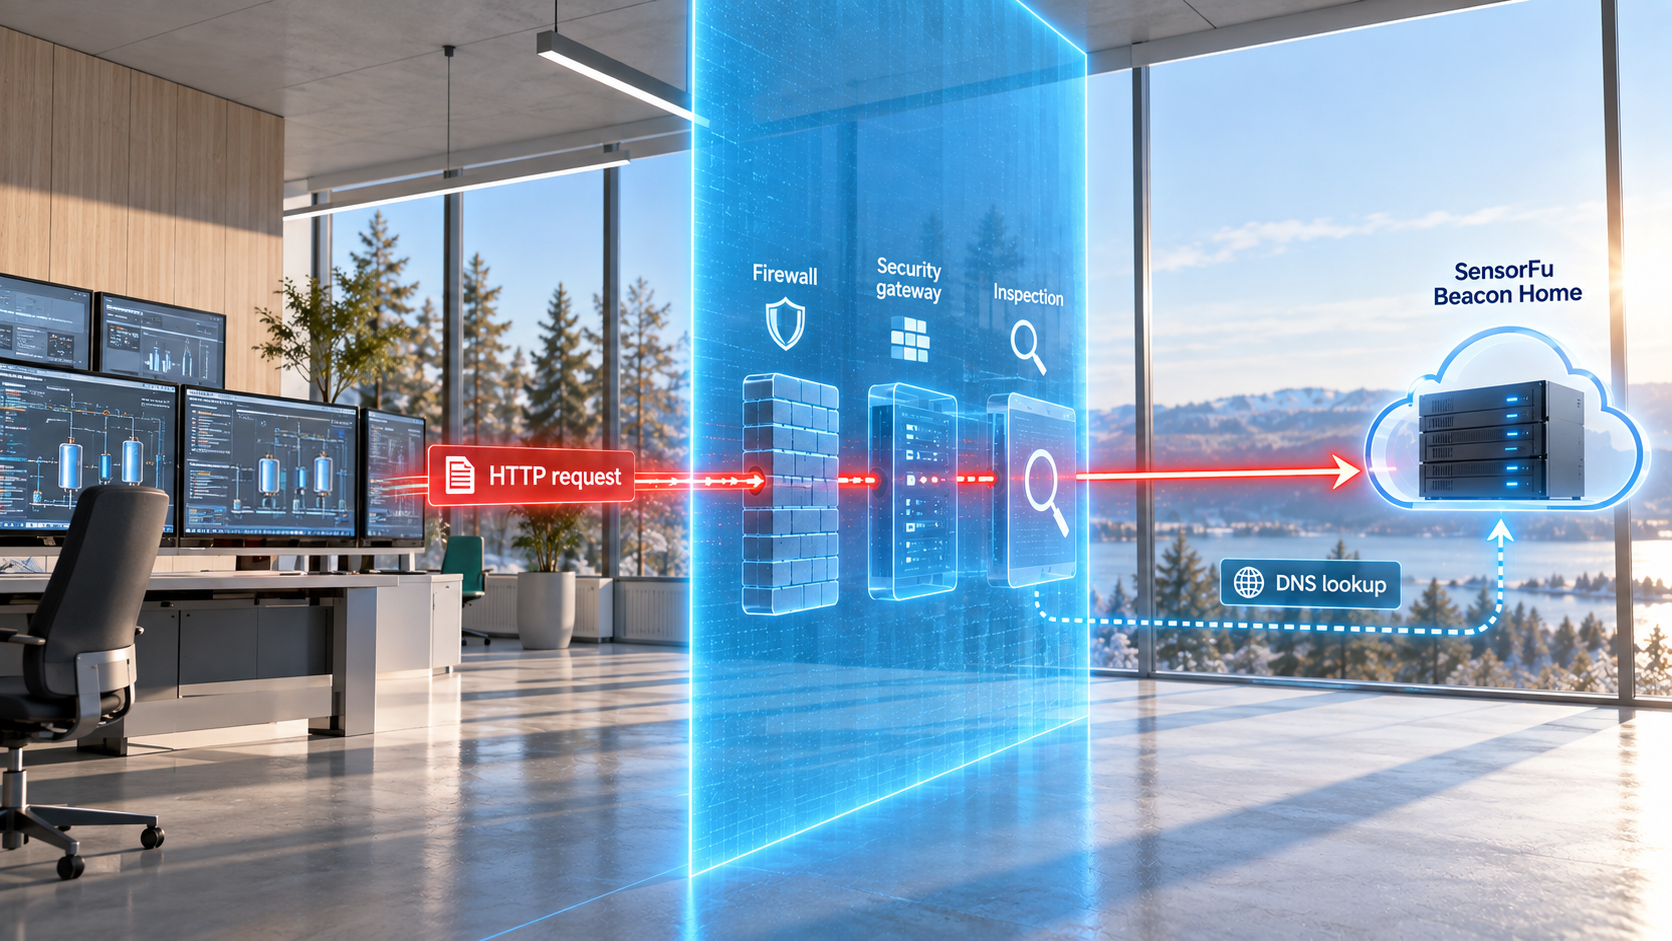
Network isolation is built on the assumption that unwanted outbound traffic can simply be blocked.
In practice, modern networks use firewalls, application-aware security controls, security gateways, and inspection systems that can treat different types of traffic in different ways.
The HTTP Escape Test was inspired by SensorFu Beacon’s earlier TLS testing. During that work, we discovered that security infrastructure inspecting outbound traffic can unintentionally create additional communication paths. This led us to explore whether the same principle could be applied to HTTP, using a legitimate HTTP request as another way to test network isolation and identify unexpected communication paths.
Using HTTP to Detect Network Isolation Failures
HTTP is the foundation of web communication, making it a natural protocol for testing network isolation. Network controls can treat traffic differently depending on the protocol, potentially blocking direct TCP connections while allowing legitimate application-level traffic.
The new HTTP test in SensorFu Beacon therefore goes beyond simply checking whether TCP port 80 is reachable. It sends a fully formed HTTP request to Beacon Home and observes whether the request can cross the network boundary. If it reaches Home, Beacon confirms that HTTP traffic can escape the isolated environment.
The test uses real HTTP communication between SensorFu Beacon and Beacon Home. Beacon sends a valid HTTP request through the network’s firewalls, segmentation controls, and application-level security systems. If Beacon Home detects the request, the request has successfully crossed the network boundary.
Beacon Home then responds back to the Beacon who reached it, allowing the chance to perform a bi-directional check, like with many of our other escapes and determine whether communication works in both directions. This provides a clearer picture of what communication is actually possible, rather than simply showing that a particular port is reachable.
Detecting Additional Communication Paths
The HTTP test also looks at how security infrastructure handles the request. The hostname in an HTTP request is carried in the Host header, which may be inspected and resolved by network security controls, creating an additional DNS-based communication path to SensorFu Home.
This means a single HTTP escape can potentially reveal two observable paths: the HTTP request reaching Beacon Home directly, and a secondary DNS-based path triggered by security infrastructure. This capability allows SensorFu Beacon to identify not only direct protocol escapes, but also covert communication channels created by the systems intended to protect the network.
Launch and feedback
We look forward to our client’s feedback on the new HTTP test now that it has been released. Keep an eye out for the update and make sure to upgrade your SensorFu Beacons!


