NIS2: Belgian organisations can continuously verify network isolation
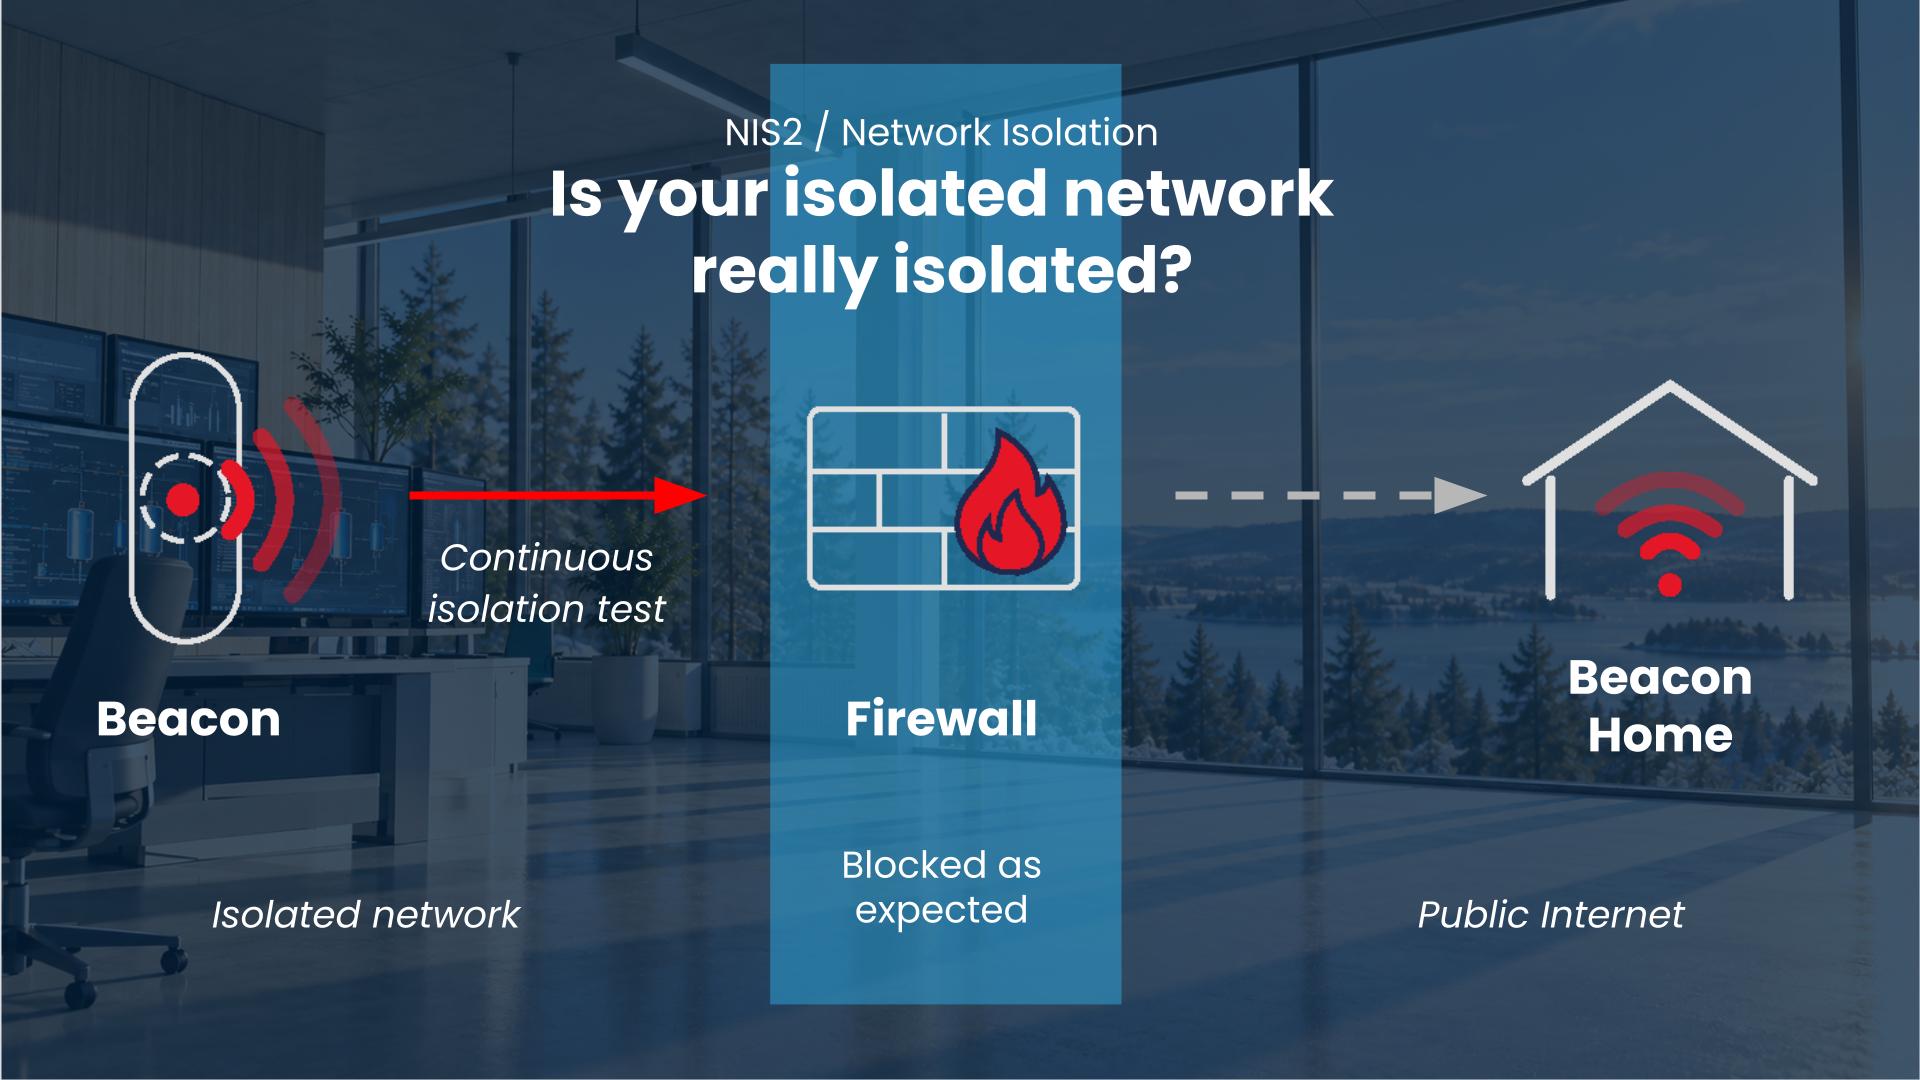
The Centre for Cybersecurity Belgium (CCB) has warned that artificial intelligence is accelerating and amplifying cyber threats, making strong cybersecurity fundamentals more important than ever and calls for organisations to strengthen their basic security measures. The CCB specifically highlights the importance of strengthening cybersecurity foundations. For Belgian organisations operating under the NIS2 framework, this message is particularly relevant.
Under Belgium’s NIS2 law, organisations must implement appropriate and proportionate cybersecurity risk-management measures to manage risks to network and information systems and prevent or minimise the impact of cyber incidents.
The CCB’s CyberFundamentals (CyFun) framework provides guidance on the cybersecurity measures relevant to NIS2. Within this broader security framework, network segmentation and isolation can help organisations separate critical systems, reduce unnecessary communication paths and limit the potential spread of a cyber incident.
Network segmentation is an important part of these cybersecurity foundations and can be an important part of an organisation’s NIS2 security measures. However, segmentation only provides protection when it works in practice.
Network Segmentation: Configured Doesn’t Always Mean Isolated
Having network segmentation in place is only part of the challenge. As networks, configurations and access paths change, organisations also need confidence that their intended security boundaries continue to work in practice.
After all, isolation only works when the boundary holds. Continuous verification helps identify unexpected connectivity between environments that are supposed to remain isolated, so organisations can spot when that boundary is no longer working as intended.
Network segmentation and isolation can weaken without anyone intentionally removing the control. Firewall rules may change, equipment may be replaced, remote-access paths may be introduced, routing can be modified, or a configuration change can create an unexpected communication path between environments.
SensorFu Beacon supports a NIS2 cybersecurity strategy
SensorFu Beacon does not make an organisation automatically NIS2 compliant. Network segmentation is one part of a broader cybersecurity risk-management programme. But it can help organisations continuously verify that an important security control and an integral part of NIS2, network isolation, is working as intended.
Beacons are placed inside isolated network segments and they continuously test whether they can reach Beacon Home, which sits outside the isolated environment. By using multiple escape methods, Beacon tests for possible paths across the network boundary and identifies unexpected connectivity when it occurs.
This provides security teams with an additional layer of assurance without relying solely on configuration reviews or periodic security assessments. It is particularly valuable in complex environments where networks, configurations and access paths change frequently, making manual verification difficult to maintain.
The goal is simple: move from “we believe it is isolated” to “we know it is isolated.”
In an increasingly complex and AI-enabled threat landscape, having security controls in place is no longer enough. Organisations need to know those controls continue to work when they are needed.


